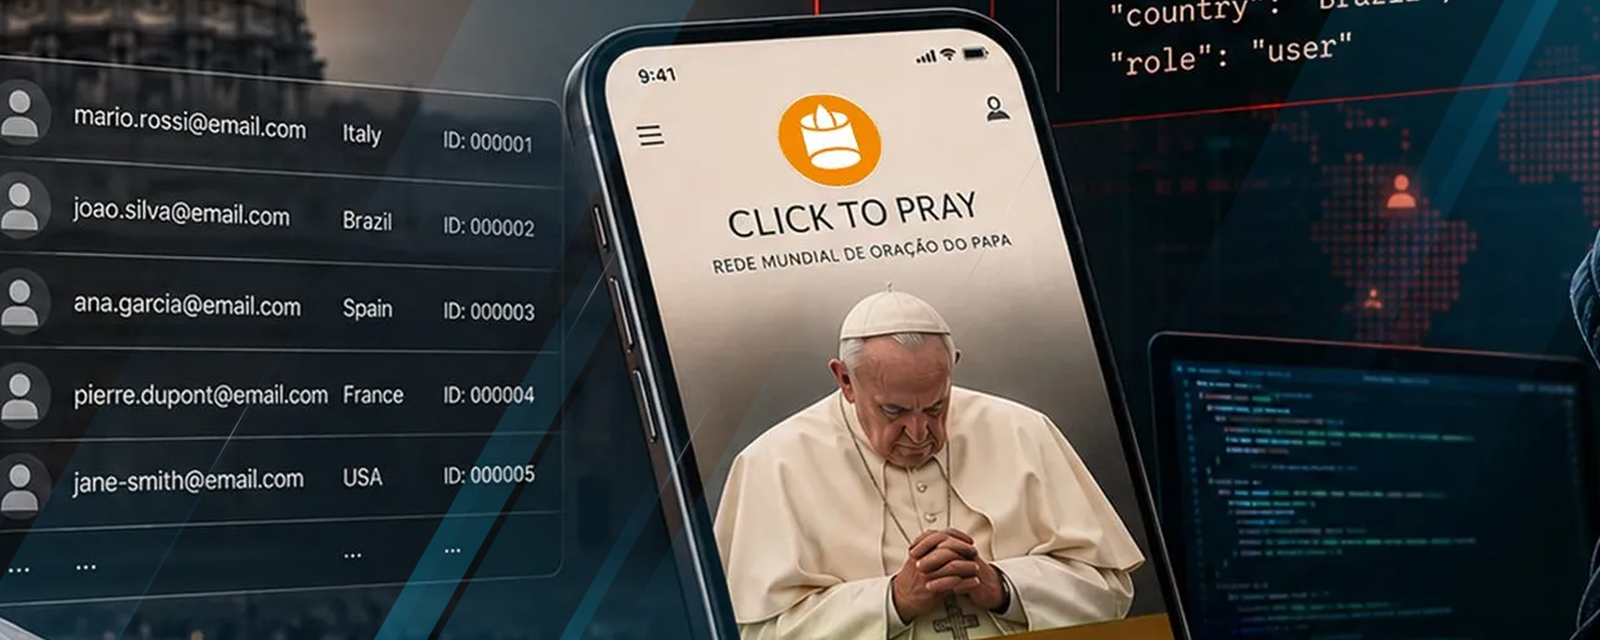
People downloaded Click to Pray for exactly what its name suggests: to pray.
The Vatican-linked platform offered daily prayers, papal content and a way for Catholics around the world to participate in the Pope’s prayer intentions.
Few users would have imagined that joining a prayer community could also expose their personal information.
But in July 2026, a serious security flaw in Click to Pray became public. The vulnerability potentially exposed personal data connected to more than 700,000 registered accounts, including names, email addresses, countries and dates of birth.
The incident is important for reasons that go far beyond the Vatican.
It demonstrates something ORCUS continues to see across the modern digital environment:
Cybercriminals do not only attack technology. They attack trust.
A Surprisingly Simple Vulnerability
The technical problem was not an advanced zero-day or sophisticated nation-state exploit.
It was much simpler.
Researchers discovered that Click to Pray assigned users sequential numerical IDs. An API used by the service allowed information associated with those IDs to be requested without properly verifying whether the person making the request was authorized to access that information.
Change the number, and the server could potentially return another person’s record.
This type of vulnerability is known as an Insecure Direct Object Reference, or IDOR — a basic access-control failure that can have serious consequences when large databases are involved.
Public reporting indicated that the platform had more than 700,000 registered accounts at the time the issue became known.
Because the account identifiers were sequential and requests could reportedly be automated, the weakness created the possibility of accessing large amounts of user information rather than targeting accounts one by one.
There is an important distinction here: public reporting established that the information was exposed, not that criminals necessarily downloaded every available record.
But exposure alone creates risk.
The Real Danger Comes After the Leak
A name and an email address may not immediately sound catastrophic.
Context changes everything.
Imagine receiving an email addressed to you by name referencing a prayer platform you actually use.
It contains Vatican branding.
It discusses a prayer initiative or account verification.
Then it asks you to sign in.
For someone who trusts the institution behind the message, there may be very little reason to question it.
That is what makes datasets like this valuable for social engineering.
The attacker doesn’t necessarily need your password from the original vulnerability. Personal information gives them the ingredients to construct a much more believable attack.
And today’s AI tools can make that process faster.
Large lists can be segmented by country, language or demographics. Messages can be personalized automatically. Fake correspondence can be written professionally and translated instantly.
An attacker can create hundreds or thousands of convincing variations instead of sending the obvious mass-phishing emails people have learned to recognize.
The more context attackers have about a victim, the more authentic the communication can appear.
When a Security Issue Remains Open
Another important part of the incident was the length of time the vulnerability reportedly remained accessible.
Public reporting indicated that the issue had been disclosed months before it was ultimately corrected.
That matters.
Security is not simply about preventing every mistake.
Mistakes happen.
What matters is whether an organization has the ability to receive a vulnerability report, understand its seriousness, escalate it and correct the problem before someone with malicious intentions discovers the same weakness.
A relatively simple access-control problem can become significantly more dangerous when it remains exposed for months.
Your Digital Security Depends on Other People’s Security
There is a larger lesson here for executives, high-net-worth individuals and families.
You can secure your phone.
You can use strong passwords.
You can enable multifactor authentication.
You can protect your home network.
And your information can still be exposed because you created an account with an organization you trusted.
A prayer app.
A hotel.
A private club.
A healthcare provider.
A school used by your children.
An airline.
A luxury service.
A charitable organization.
Every organization that holds information about you becomes part of your extended digital attack surface.
The more prominent the individual, the more useful these small pieces of information become when they are combined.
An email address from one breach, a phone number from another database, a family relationship from social media and travel information from somewhere else can eventually become a remarkably detailed profile of a target.
That is why personal cybersecurity cannot end with protecting devices.
It requires understanding where your identity exists, who holds your information and how exposed that information has become.
Trust Is Now a Security Credential
Click to Pray was built around one of the strongest forms of human trust: faith.
That is exactly why incidents like this matter.
The most convincing cyberattack may not arrive from a suspicious stranger.
It may appear to come from your bank.
Your attorney.
Your assistant.
Your child’s school.
Your family office.
Or even an institution you have trusted your entire life.
Technology will continue to change.
The basic principle attackers exploit has not.
The more you trust the sender, the less likely you are to question the message.
In modern cybersecurity, protecting that trust has become just as important as protecting the password.
ORCUS | Digital Executive Protection
ORCUS protects high-net-worth individuals, executives and family offices beyond the traditional corporate perimeter — across personal devices, accounts, identities and the digital relationships attackers increasingly use to reach their targets.